Welcome to our Trust Center.
The EASE platform has been designed for 360° security. We’re dedicated to keeping
your company and user data safe, while ensuring you have complete transparency of our security policies.
Compliance is a top priority.
The EASE platform is fully compliant with SOC II, GDPR, and ITAR standards, demonstrating our commitment to setting the highest security standards and building best-in-class practices. Every year, we validate our security with 3rd party application and penetration testing against our production environments.

User & device authentication.
When users log in, an authentication token is issued with a limited valid lifetime that varies according to environment and device type. The EASE platform also supports Single Sign-On (SSO) with most Identity Providers (IdP) to enable advanced authentication services like MFA.

Authorization & access controls.
Our web pages and web service API calls require an authenticated identity and specific role membership(s) for a user to access certain resources — based on your administrator’s assignment of permissions to a specific user.
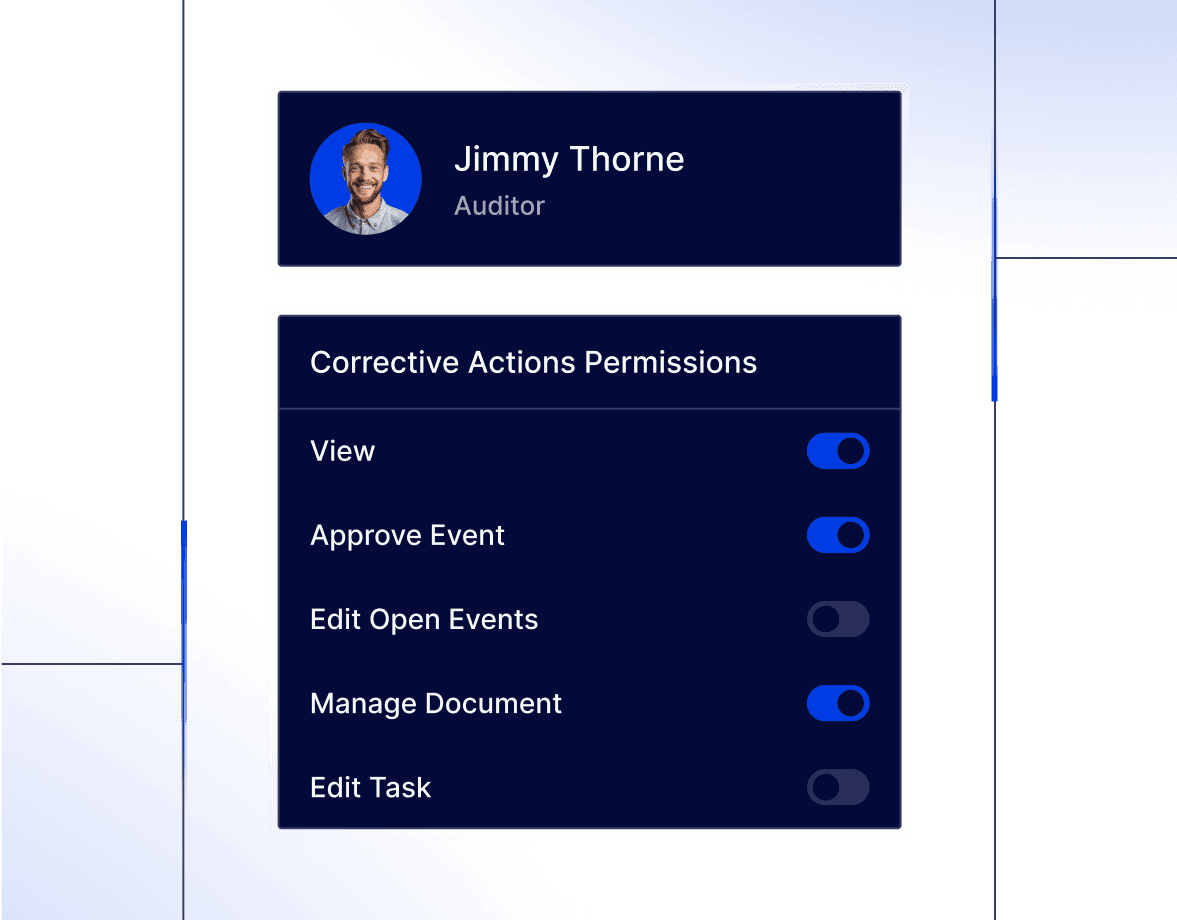
Rock-solid account protection.
User passwords are stored securely in our database using a one-way hash value, making decryption impossible. We enforce minimum password rules during changes. Authentication is fortified against CSRF with token usage, and our system implements throttling to prevent DDoS attacks.

Traffic & document encryption.
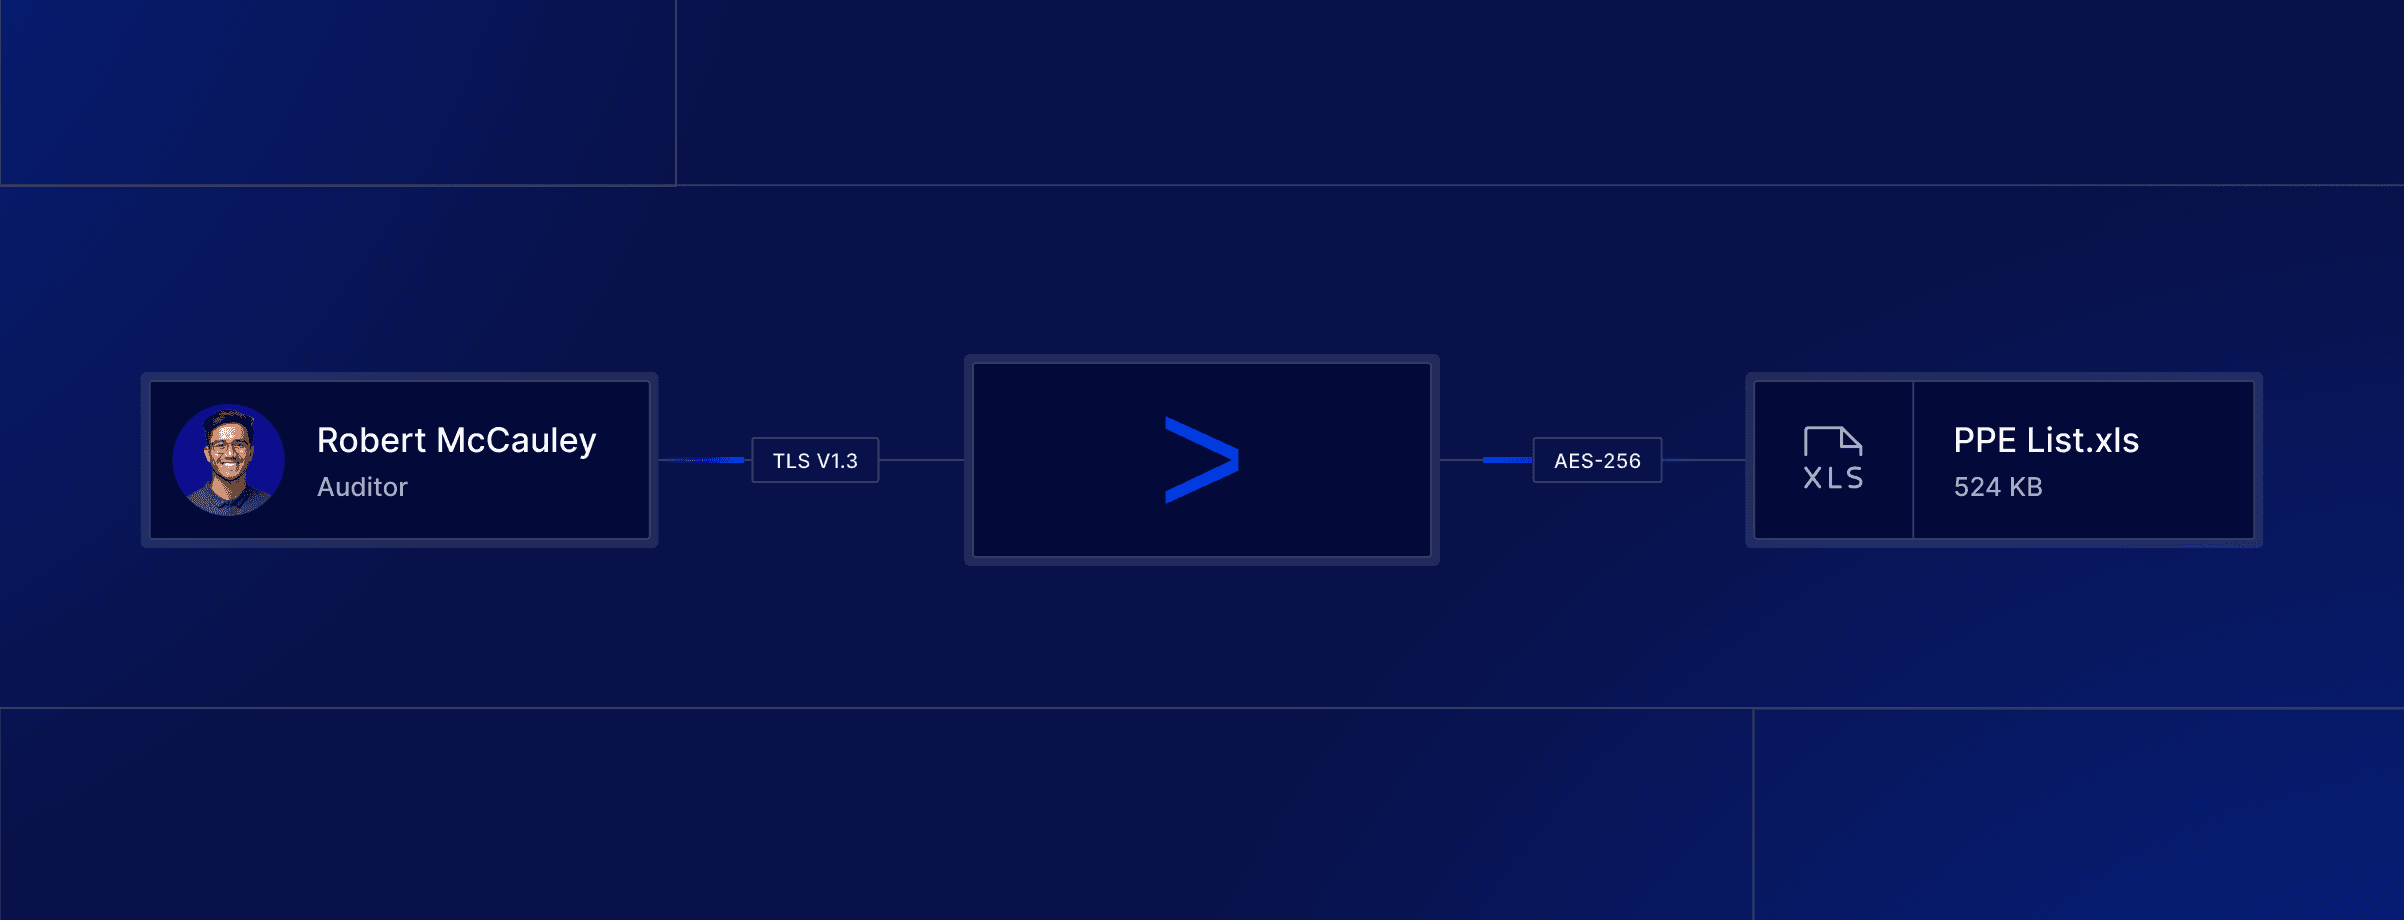
Web browser access via TLS v1.3 is used to encrypt data traffic between the users and EASE. All traffic between users and our platform is encrypted in transit. We review our SSL ciphers regularly and disable any weak ciphers. And all documents and attachments are automatically encrypted using the AES-256 encryption process.
Common Questions
EASE maintains a commitment to rigorous compliance standards and is fully compliant with SOC II, GDPR, and ITAR standards, assuring the security, availability, and confidentiality of your data based on controls examined by independent third-party auditors. We also adhere to data protection regulations like GDPR. For specific regulatory requirements (like CQI, ISO 9001, etc.), EASE provides the tools and audit trails necessary for you to maintain your certifications.
Data protection is paramount. EASE enforces enterprise-grade encryption measures:
In Transit (Data Security): All communication between your devices and the EASE cloud platform is secured using Transport Layer Security (TLS 1.2 or higher) encryption, preventing interception.
At Rest (Data Storage): Your sensitive quality data, including findings and action plans, is stored using Advanced Encryption Standard (AES-256) encryption on secure cloud infrastructure, guaranteeing confidentiality and integrity.
Yes, EASE fully supports both Single Sign-On (SSO) and Multi-Factor Authentication (MFA) to meet corporate security mandates through Security Assertion Markup Language (SAML). This allows users to access EASE using their existing company credentials, enforcing centralized security policies and reducing password fatigue.
User access is controlled via a role-based access control (RBAC) system that is granular and fully configurable. Administrators can assign users specific roles and scopes which govern:
- Which sites/locations a user can access.
- Which checklists/audit types a user can schedule or complete.
- The level of access to data (view, edit, delete) within reports and action plans.
This ensures that users only interact with the data relevant to their role and location.
EASE utilizes centralized Reporting and Dashboards to provide instant, real-time visibility. Managers and leadership can view a consolidated table that displays the status of all Corrective Actions (CAPAs)—including overdue, in-progress, and completed—filtered by department, facility, process, or non-conformance type. Crucially, EASE offers data export to make this rich action plan data available for integration into your existing Business Intelligence (BI) tools like Power BI, Tableau, and Qlik, allowing you to merge quality data with other business metrics for deeper analysis.
Yes. Maintaining a strong security posture requires continuous evaluation. EASE engages independent, certified third-party security firms to conduct regular penetration testing and security audits on the platform. Any identified vulnerabilities are addressed immediately, ensuring the security of the platform is continuously validated against industry best practices.
EASE provides solutions for operating in the Greater China region. Given the specific regulatory and network requirements in China, EASE offers deployment options designed to support stable performance and data residency requirements for our multi-national customers operating in the region. We work with clients to ensure a compliant and reliable rollout in China.
You retain 100% ownership of all your quality data uploaded to the EASE platform. EASE acts only as the secure custodian and processor of that data. To ensure data portability, EASE provides export capabilities (via reports, CSVs, API, and EASE Connect) that allow you to extract all your historical audit findings, action plans, and configuration data at any time, providing a clear SaaS exit strategy and peace of mind.